INTEGRATION
FortiGate Captive Portal
Integration
FortiGate secures your network. It does not turn the guest SSID into a branded experience or a marketing asset. Useroam sits on top of the Fortinet stack you already run and does exactly that.
What the FortiGate integration does
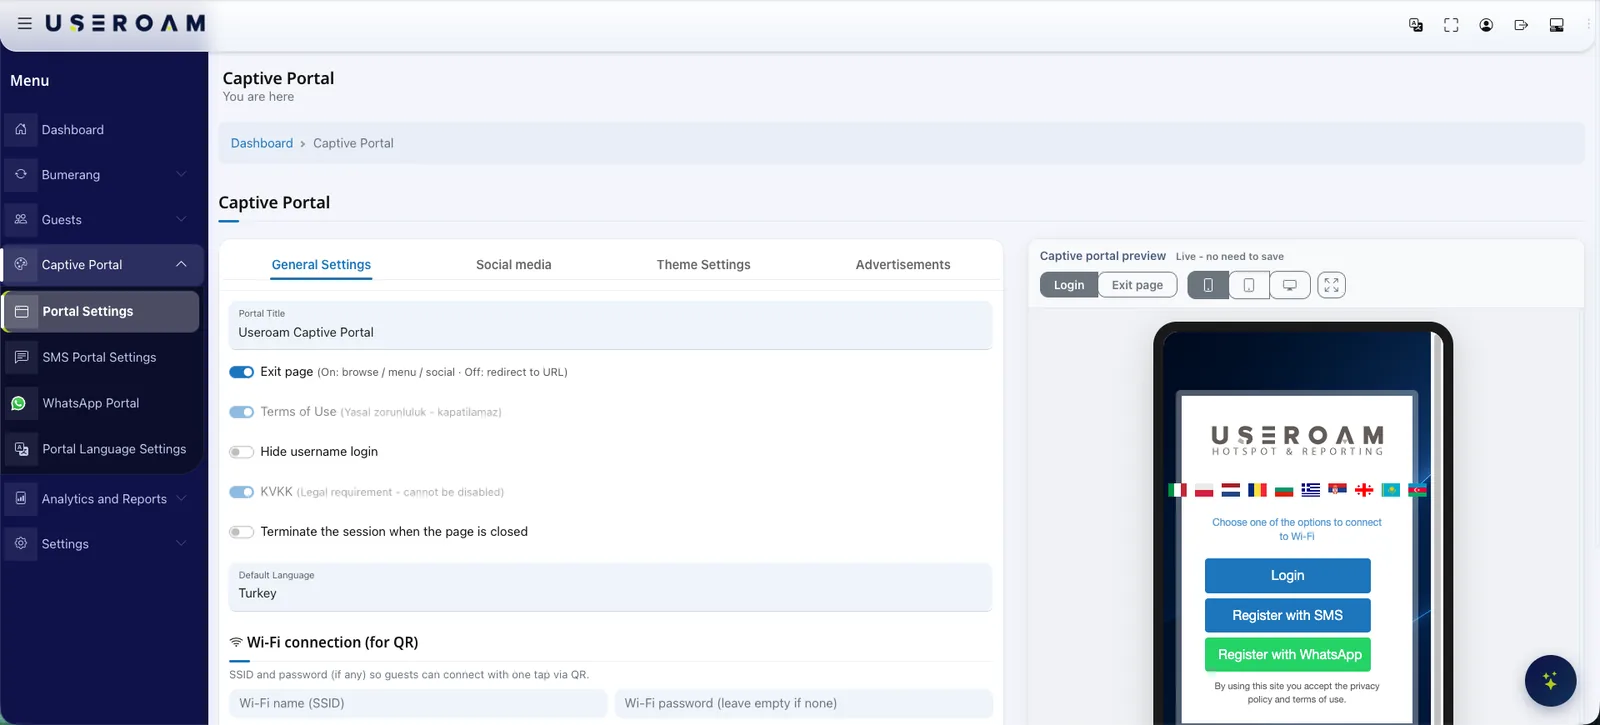
Useroam Cloud picks up the user connecting to the guest network defined on your FortiGate, hands them an external captive portal in your brand, verifies who they are and keeps their access records. Guests sign in with a one-time code over SMS or WhatsApp, a voucher, a room number and surname in hotels, or a username and password; RADIUS authorises the session and per-user speed, quota and time rules follow from the same panel. Access records are forwarded from the FortiGate over syslog, signed daily with an RFC 3161 timestamp from an accredited timestamp authority and retained for the period local regulation requires, so there is no logging server to build, maintain or back up. The same flow runs on FortiGate, FortiGate-VM, FortiWiFi and FortiAP deployments, and your existing Fortinet policies stay exactly as they are — only the external portal and syslog definitions are added for the guest network.
How the integration works
Guest SSID and external portal
A guest SSID and external captive portal are configured on the FortiGate; unauthenticated traffic is redirected to the Useroam Cloud portal.
Portal and walled garden
A branded welcome page is designed in Useroam Cloud; the portal and verification services are added to the walled garden so they stay reachable before login.
RADIUS authorisation
The guest verifies their identity over SMS or WhatsApp; the verified mobile number becomes the RADIUS username for the session and the firewall authorises access.
Syslog and signed logs
Access and NAT records are collected from the firewall over syslog, signed daily with an RFC 3161 timestamp from an accredited timestamp authority and retained for the period local regulation requires. Any record needed for an audit is served from the panel.
The welcome screen carries your brand
The captive portal is designed in the panel with your logo, colours and background image, and published with a live per-device preview. The same screen doubles as a placement for your campaigns and announcements.
What to know on the FortiGate side
- Compatible with physical FortiGate models and FortiGate-VM virtual deployments.
- FortiAP and FortiWiFi access points managed through the FortiGate are supported; the SSID can be broadcast in local or tunnelled mode.
- The guest network is governed by its own security policy, separate from corporate traffic — your internal security posture is unchanged.
A marketing layer on the same network
The FortiGate integration is not only about getting guests online: every guest who connects becomes permissioned data. The Bumerang modules run from the same panel, with no additional deployment.
Campaigns
Welcome and win-back flows go out automatically over WhatsApp/SMS, and the return visit is measured in the panel.
Surveys
Happy guests are routed to a Google review, unhappy feedback comes to you — your reputation is fed by the WiFi.
QR Menu
Multilingual menu and order-from-table, with reporting on which item drew interest and when.
Other integrations
Useroam is vendor-agnostic: even when sites run different devices, everything is managed from one panel.
Your hardware is ready. Let's open the guest network.
Send us your model and we will plan the integration steps together and open a demo environment the same day.
Frequently asked questions
Do I need extra hardware or a licence for FortiGate guest WiFi?
How are access logs handled?
Does it work with FortiAP and FortiWiFi, and will my policies change?
Related guides
Firewall Guest WiFi Integrations: Sophos, FortiGate & More
A brand-by-brand look at how guest WiFi authentication and logging integrate with Sophos, FortiGate, Palo Alto, Zyxel and MikroTik — and how to choose.
What Is a Captive Portal and How Does It Work?
The captive portal is the sign-in screen guests see when they join your WiFi. Here is how it works, what it does for your business and why cloud-based portals win.