INTEGRATION
Cisco Catalyst 9800 Captive Portal
Integration
A Catalyst 9800 controller broadcasts the guest network. What it does not give you is a branded welcome screen, verified guest identity or a guest database you can market to. Useroam adds that layer through external web auth and RADIUS — your controller stays exactly where it is.
What the Cisco Catalyst 9800 integration does
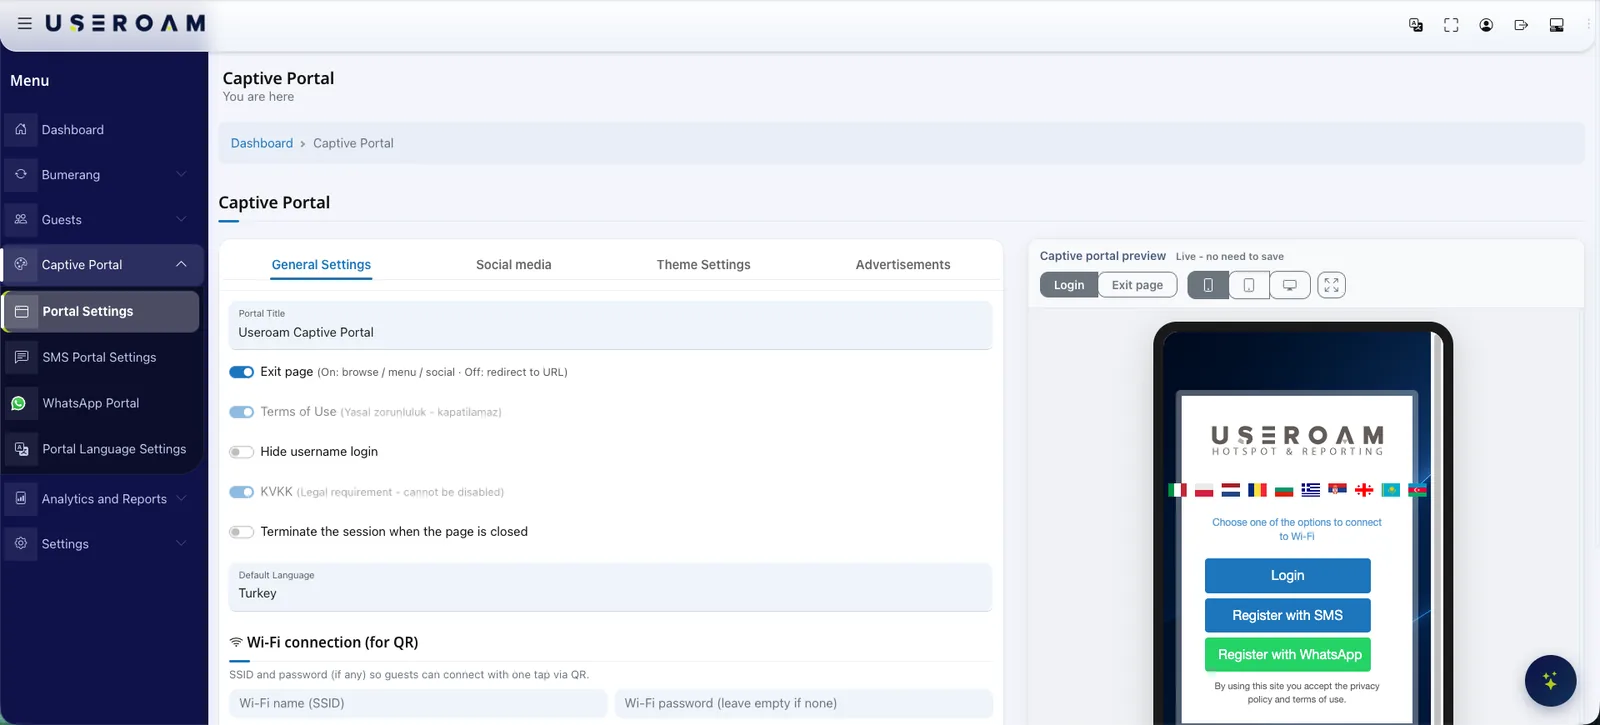
Useroam Cloud takes the guest joining the open guest WLAN on a Catalyst 9800 controller, presents a captive portal carrying your brand and verifies their identity. On the controller the guest WLAN is bound to the useroam-portal web auth parameter map through Layer 3 Web Policy, with a pre-authentication ACL that keeps DHCP, DNS and the portal reachable before login. Guests sign in with a one-time code over SMS or WhatsApp, a voucher, a room number and surname in hotels, or a username and password; authentication runs over RADIUS on port 1812 and accounting arrives on 1813, filling the active-guest list and usage reports in the panel. Interim accounting updates every five minutes, and the records carry the MAC address of the access point the guest joined along with the SSID, so you can read which AP served which session. Session and idle timeouts are set on the policy profile. Access records are collected over syslog from the device handling internet egress, signed daily with an RFC 3161 timestamp from an accredited timestamp authority and retained for the period local regulation requires — no appliance and no on-site logging server.
How the integration works
External web auth and RADIUS
An open guest WLAN is created on the controller; Layer 3 Web Policy binds the useroam-portal parameter map and the USEROAM-PREAUTH pre-authentication ACL, so unauthenticated guests are redirected to the Useroam login page.
Portal and walled garden
A branded welcome page is designed in Useroam Cloud; the portal and verification services are added to the walled garden so they stay reachable before login.
RADIUS authorisation
The guest verifies their identity over SMS or WhatsApp; the verified mobile number becomes the RADIUS username for the session and the controller authorises access. Accounting records feed the active-guest list and usage reports in the panel.
Syslog and signed logs
The firewall or router handling internet egress forwards access records to Useroam over syslog; they are signed daily with an RFC 3161 timestamp from an accredited timestamp authority and retained for the period local regulation requires. Where the controller is not the egress device, that device is the log source.
The welcome screen carries your brand
The captive portal is designed in the panel with your logo, colours and background image, and published with a live per-device preview. The same screen doubles as a placement for your campaigns and announcements.
What to know on the Cisco Catalyst 9800 side
- Works with Catalyst 9800 series controllers, including the virtual 9800-CL, on IOS-XE 17.x releases.
- The controller's public egress IP address is registered in the panel and RADIUS requests must originate from it; private addresses (10.x, 192.168.x) are not accepted.
- In the global web auth settings the HTTP server must be enabled and secure (HTTPS) web auth disabled, otherwise the guest browser never submits the login to the controller.
- If WhatsApp sign-in is used, the Meta IP ranges are added to the pre-authentication ACL. The full step-by-step setup lives in the Cisco Catalyst 9800 WLC guide in the help centre.
A marketing layer on the same network
The Cisco Catalyst 9800 integration is not only about getting guests online: every guest who connects becomes permissioned data. The Bumerang modules run from the same panel, with no additional deployment.
Campaigns
Welcome and win-back flows go out automatically over WhatsApp/SMS, and the return visit is measured in the panel.
Surveys
Happy guests are routed to a Google review, unhappy feedback comes to you — your reputation is fed by the WiFi.
QR Menu
Multilingual menu and order-from-table, with reporting on which item drew interest and when.
Other integrations
Useroam is vendor-agnostic: even when sites run different devices, everything is managed from one panel.
Your hardware is ready. Let's open the guest network.
Send us your model and we will plan the integration steps together and open a demo environment the same day.
Frequently asked questions
Do I need extra hardware or a licence for Cisco guest WiFi?
How are access logs handled on Cisco?
What if the controller sits behind a firewall?
Related guides
Firewall Guest WiFi Integrations: Sophos, FortiGate & More
A brand-by-brand look at how guest WiFi authentication and logging integrate with Sophos, FortiGate, Palo Alto, Zyxel and MikroTik — and how to choose.
What Is a Captive Portal and How Does It Work?
The captive portal is the sign-in screen guests see when they join your WiFi. Here is how it works, what it does for your business and why cloud-based portals win.